otx.alienvault.com
Community threat intelligence platform for indicators, pulses, malware, and attack research.
Directory
Published directory entries matching your search.
Community threat intelligence platform for indicators, pulses, malware, and attack research.
Insikt Group is the research unit of Recorded Future. It conducts research on cybercrime, state-sponsored threats and global issues, and supplies analyst-validated data, analytics and cyber and geopolitical intelligence to the Recorded Future Platform. Its resources include intelligence reports, threat briefings and information on threat actors.

Cisco Talos Intelligence Group is a threat intelligence operation that publishes threat research and an Intelligence Center with web reputation, content categorization, sender IP and domain reputation, file reputation and IPS/IDS resources. It also offers incident response services for emergency network security needs and proactive intelligence-led services.

ThreatMap is a developer resource for coding, documentation, communities, security research, or software tools.
GitHub collection of APT reports, threat actor notes, and security research documents.
Research and explainers on dark-web investigations, criminal forums and threat-intelligence methods.
Threat intelligence resource board with links for indicators, malware, security research, and monitoring.
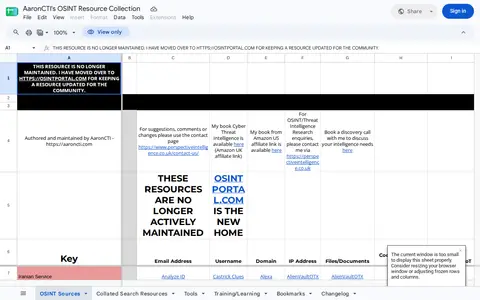
This is a no-longer-maintained Google Sheets resource collection compiled by AaronCTI, with its updated version hosted at OSINTPORTAL.COM. It categorizes links to cyber threat intelligence and open source intelligence resources for lookups including email addresses, IP addresses, social media profiles, and data breaches.
A blog from DarkOwl whose analysts publish insights on darknet intelligence, threat detection and cybersecurity trends. Posts include a darknet marketplace snapshot series and articles on breach data and ransomware. The blog states it offers news, research and resources for enterprises and security professionals.

The IUCN Red List of Threatened Species is a source of information on the global conservation status of animal, fungi and plant species used to inform biodiversity conservation and policy. The extract states the list divides species into nine categories, including Not Evaluated and Data Deficient.
Threat intelligence search platform for malware indicators, IPs, domains, URLs, and hashes.
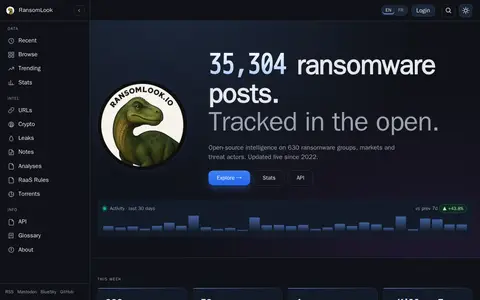
RansomLook is an open-source intelligence site that tracks ransomware groups, markets and threat actors, displaying posts and activity statistics. It reports 35,915 ransomware posts across 634 groups, 147 markets and 32 actors, alongside leak, ransom note and crypto address counts. An API and torrent intelligence features are listed.
GitHub awesome list collecting OSINT tools, datasets, training links, and research resources.

Malware research archive with papers, samples, writeups, and historical security material.

BioVeL is an evidence-based biodiversity science reference resource. It provides clear coverage of key topics including population ecology, types of biodiversity, 36 global conservation hotspots, threats to wildlife and associated research workflows. The reference includes information on over 8.7 million described species and more than 1 million threatened species.

eCrime.ch is an extortion exposure monitoring platform for enterprise security, incident response and third-party risk teams. It detects, verifies and delivers ransomware and data-leak signals with context such as entity mapping, artifacts, links and timelines. The site states it monitors 280+ extortion and leak sources and delivers alerts through dashboard, email, Slack, API and reports. A REST API provides tracker, intelligence, file-search, screenshot, actor, leak-site and torrent-monitoring data.
The European Soil Data Centre (ESDAC) is a resource hosted by the European Commission Joint Research Centre, focused on soil-related data and knowledge. It is part of the EU Soil Observatory, and provides datasets, maps, documents and indicators covering topics including soil properties, erosion and soil threats.
Exploit-DB paper archive with security research, exploitation papers, and technical writeups.
Exploit-DB binary exploit archive for security research and controlled testing.
Research articles on dark-web monitoring, exposed data, cybercrime groups and external threats.
Malpedia is a free service from Fraunhofer FKIE aimed at providing a resource for rapid identification and actionable context when investigating malware. Curated contributions are intended to support accountable quality and reproducible research. Not all content is publicly available; an account is needed to access all data, such as malware samples and non-public YARA rules, and it is operated as an invite-only trust group.
GitHub malware research repository containing live samples for controlled analysis environments.
OSINT toolkit board collecting research links, search tools, and investigation resources.

UNODC report on darknet-enabled cybercrime threats and policy responses in Southeast Asia.