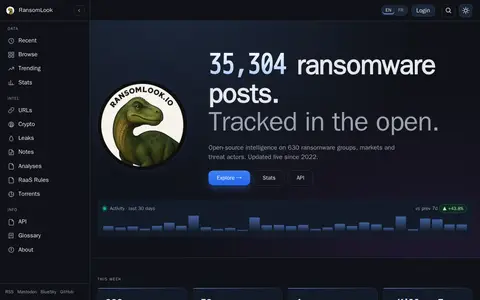
RansomLook is an open-source intelligence site that tracks ransomware groups, markets and threat actors, displaying posts and activity statistics. It reports 35,915 ransomware posts across 634 groups, 147 markets and 32 actors, alongside leak, ransom note and crypto address counts. An API and torrent intelligence features are listed.
eCrime.ch
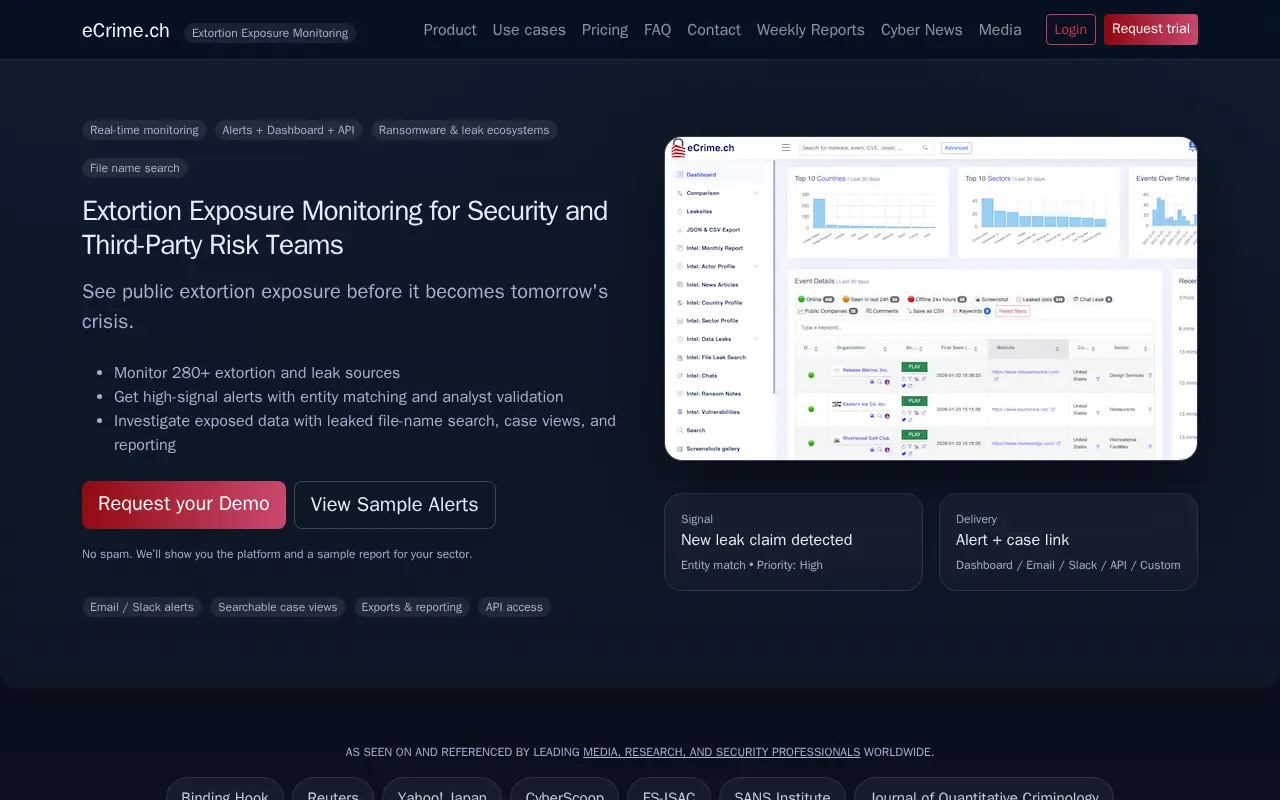
eCrime.ch is an extortion exposure monitoring platform for enterprise security, incident response and third-party risk teams. It detects, verifies and delivers ransomware and data-leak signals with context such as entity mapping, artifacts, links and timelines. The site states it monitors 280+ extortion and leak sources and delivers alerts through dashboard, email, Slack, API and reports. A REST API provides tracker, intelligence, file-search, screenshot, actor, leak-site and torrent-monitoring data.
Features
- REST API for tracker, intelligence, file-search, screenshot, actor, leak-site, torrent-monitoring data Source: ecrime.ch
Links
Tags
-
0RansomLook is an open-source intelligence site that tracks ransomware groups, markets and threat actors, displaying posts and activity statistics. It reports 35,915 ransomware posts across 634 groups, 147 markets and 32 actors, alongside leak, ransom note and crypto address counts. An API and torrent intelligence features are listed.
-
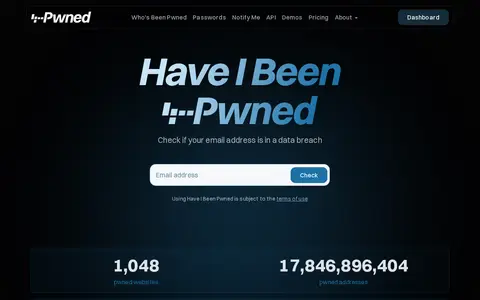
0Have I Been Pwned is a data breach search and notification service. It lets users check whether an email address appears in known data breaches and lists instances where data was found in paste records. It also offers an MCP server that connects AI agents to breach, password, paste, domain and stealer log data.
-
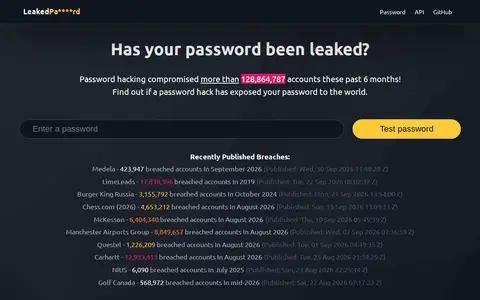
0Leakedpassword.com searches across multiple data breaches to check whether a password has been compromised. It also provides an API for use in signup processes to validate users' passwords, drawing its data from Have I Been Pwned and requiring no authentication.
-
0
Open-source tracker monitoring ransomware leak sites and publishing structured status data.
-
0
A tool for checking whether an email address appears in the Ashley Madison breach data. The site states about 36 million accounts were compromised, including some duplicate email addresses, and advises changing passwords. It also notes that Ashley Madison did not validate account email addresses.
-
0Bloomberg Industry Group accepts confidential news tips through SecureDrop, described as a secure communication platform designed to protect anonymity. Bloomberg Industry Group controls the server, which stores submitted information in encrypted form. The page advises against using home, office or employer networks and devices, recommending public wifi and devices the source controls. Signal and postal mail are listed as alternative methods.
Community notes
Reviews and discussion
No reviews yet
Be the first to share how this project worked for you.
Join the discussion
Sign in with a verified account to leave a review or join the discussion.
Sign in to review