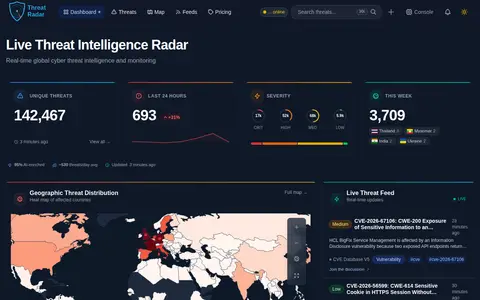
Threat Radar is a real-time cyber threat intelligence radar showing vulnerabilities, malware, and global cyber threats, vulnerabilities, and attack patterns. It offers a live threat feed, geographic threat distribution, a threat timeline, and a REST API for access to threat intelligence data. A free account provides 30 API requests per hour.
Directory
Search results
Published directory entries matching your search.
NETSCOUT Cyber Threat Horizon offers a real-time DDoS attack map and threat statistics. The site presents a customizable view of the global cyber threat landscape, with attack map, statistics and expert analysis sections, plus filters for event values, sources, destinations and event types.
Cisco Talos Intelligence Group is a threat intelligence operation that publishes threat research and an Intelligence Center with web reputation, content categorization, sender IP and domain reputation, file reputation and IPS/IDS resources. It also offers incident response services for emergency network security needs and proactive intelligence-led services.
Community threat intelligence platform for indicators, pulses, malware, and attack research.
Threat map from FireEye/Mandiant showing cyber activity and attack visualization data.
Fortinet map visualizing cyber attack activity, malware detections, and global threat events.
Check Point live map visualizing cyber attacks and threat activity by region.
LookingGlass threat map for visualizing security events, attack activity, and internet risk signals.
Feedly Threat Intelligence is a platform for collecting, analyzing and sharing cyber threat intelligence such as vulnerabilities, cyberattacks, threat actors and IoCs. It gathers signals from over 10,000 clear and dark web sources and includes AI tools and integrations that deliver STIX-formatted intelligence. The service is offered in Standard and Advanced plans.
Insikt Group is the research unit of Recorded Future. It conducts research on cybercrime, state-sponsored threats and global issues, and supplies analyst-validated data, analytics and cyber and geopolitical intelligence to the Recorded Future Platform. Its resources include intelligence reports, threat briefings and information on threat actors.
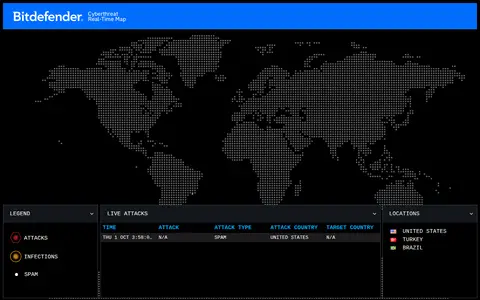
Bitdefender map showing detected cyber threats, malware activity, and attack trends.
Pulsedive is a free threat intelligence platform for searching, scanning and enriching IPs, URLs, domains and other IOCs from OSINT feeds or submitted data. It supports on-demand passive or active scans and a query language for pivoting across indicators and threats, with export options. Paid tiers are listed for non-commercial and commercial use, including API and feed access.
Cisco Talos Intelligence operates an IP and Domain Intelligence Center for real-time threat detection. It publishes threat data including daily volume and volume change metrics for top email and spam sending countries. The service also accepts incident response inquiries for emergency network security needs.
This is a no-longer-maintained Google Sheets resource collection compiled by AaronCTI, with its updated version hosted at OSINTPORTAL.COM. It categorizes links to cyber threat intelligence and open source intelligence resources for lookups including email addresses, IP addresses, social media profiles, and data breaches.
Threat intelligence search service for checking IPs, domains, hashes, and security indicators.
Fortinet threat intelligence portal for security updates, IP reputation, malware, and web filtering data.
Open source threat intelligence platform for analyzing observables, files, and security indicators.
Criminal IP is a threat intelligence platform. It delivers AI-powered threat intelligence, IP reputation analysis, attack surface management, fraud detection, and brand protection. Users can use it to discover exposed assets, detect malicious infrastructure, and reduce cyber risk in real time.
CrowdSec provides curated, crowd-powered threat intelligence in the form of actionable blocklists intended to help security operations teams block malicious IPs. The site describes a global view of threat intelligence built from data from real users, servers and production environments, and lists blocklists covering aggressive IPs, specific industries and countries, and high background noise.
A blog from DarkOwl whose analysts publish insights on darknet intelligence, threat detection and cybersecurity trends. Posts include a darknet marketplace snapshot series and articles on breach data and ransomware. The blog states it offers news, research and resources for enterprises and security professionals.
RansomLook is an open-source intelligence site that tracks ransomware groups, markets and threat actors, displaying posts and activity statistics. It reports 35,915 ransomware posts across 634 groups, 147 markets and 32 actors, alongside leak, ransom note and crypto address counts. An API and torrent intelligence features are listed.
Research and explainers on dark-web investigations, criminal forums and threat-intelligence methods.
Threat intelligence search engine for domains, IPs, hashes, malware, and related indicators.
Threat intelligence resource board with links for indicators, malware, security research, and monitoring.