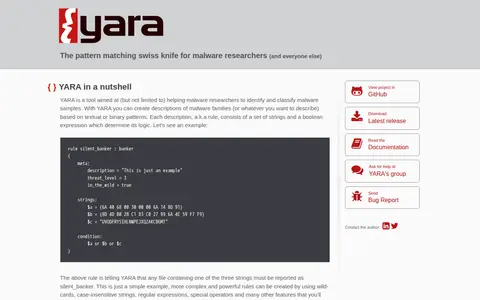
YARA is a tool aimed at helping malware researchers identify and classify malware samples. It creates descriptions of malware families, called rules, based on textual or binary patterns; each rule consists of strings and a boolean expression. YARA is multi-platform, running on Windows, Linux and Mac OS X, and can be used via its command-line interface or from Python scripts with the yara-python extension.
Directory
Search results
Published directory entries matching your search.
Filters
virustotal.github.io
github.com
Yara is a code project with source, releases, documentation, or setup notes.
malpedia.caad.fkie.fraunhofer.de
Malpedia is a free service from Fraunhofer FKIE aimed at providing a resource for rapid identification and actionable context when investigating malware. Curated contributions are intended to support accountable quality and reproducible research. Not all content is publicly available; an account is needed to access all data, such as malware samples and non-public YARA rules, and it is operated as an invite-only trust group.