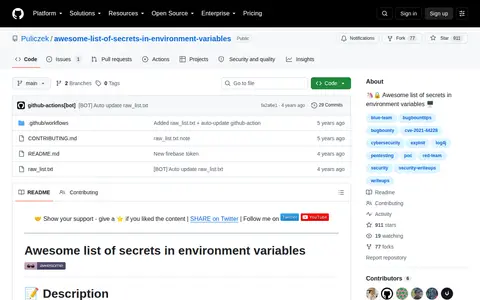
A GitHub repository listing secrets, passwords, API keys and tokens commonly stored in system environment variables. It notes that attackers can read environment variable values through exploits such as CVE-2021-44228 JNDI log4j and suggests practices to avoid leaks, including blocking requests containing system environment variables and storing paths to config files instead of clean values.
Directory
Search results
Published directory entries matching your search.