Dylib Hijack Scanner (DHS) is a macOS utility that scans a computer for applications susceptible to dylib hijacking or already hijacked. It supports macOS 11+ and favors reporting false positives over suppressing false negatives; scan options include full scan, weak hijacker detection and saving results as JSON.
Yubikey Full Disk Encryption
Yubikey Full Disk Encryption is an open source Linux, macOS, or Unix resource with code, tools, or setup notes.
Links
Tags
-
0Dylib Hijack Scanner (DHS) is a macOS utility that scans a computer for applications susceptible to dylib hijacking or already hijacked. It supports macOS 11+ and favors reporting false positives over suppressing false negatives; scan options include full scan, weak hijacker detection and saving results as JSON.
-
0Shufflecake is a Free/Libre and open-source Linux tool for creating multiple hidden encrypted volumes on a storage device, scrambled across existing storage space and indistinguishable from random noise when not decrypted. It aims to provide plausible deniability for hidden filesystems. The software is experimental and the project advises against relying on its security for important use.
-
0An ArchWiki page describing how to securely wipe a disk by writing new data over every bit. It covers common uses such as wiping all data before a device is given away or sold, and preparing a drive for block device encryption using random data.
-
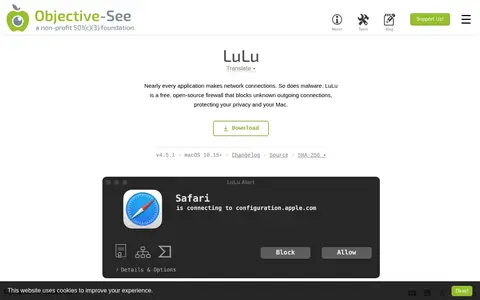
0LuLu is a free, open-source macOS firewall that blocks unknown outgoing network connections. It alerts users when a new or unauthorized outgoing connection is created, which may indicate a newly installed application or malware. Installation requires manual approval of its System Extension and Network Filter through macOS, and it runs from the status bar, starting automatically at login.
-
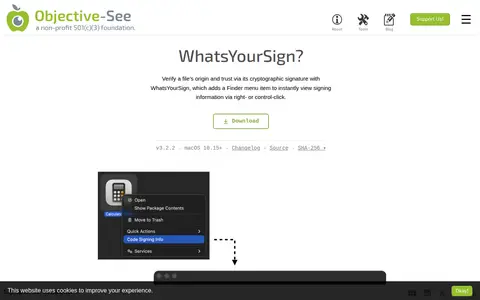
0What's Your Sign is a macOS utility that adds a Finder menu item for viewing any file's cryptographic signing information via right- or control-click. It shows details about the file's cryptographic signature, or lack thereof, including files signed by Apple. It runs on macOS 10.15 and later.
-
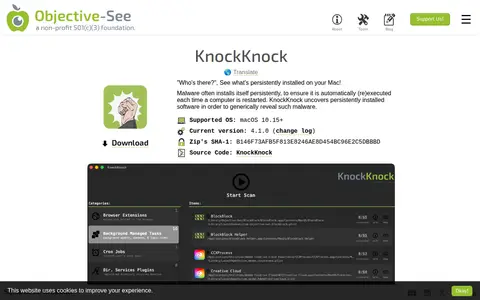
0KnockKnock is a macOS application that lists persistently installed software to reveal malware that installs itself persistently. It enumerates known locations where persistent software may be installed. Signed Apple binaries are filtered out by default, and legitimate third-party software is also displayed. It requires macOS 10.15 or later and can optionally use a VirusTotal API key.
Community notes
Reviews and discussion
No reviews yet
Be the first to share how this project worked for you.
Join the discussion
Sign in with a verified account to leave a review or join the discussion.
Sign in to review