app.any.run
ANY.RUN sandbox for interactive malware analysis, behavior monitoring, and file investigation.
Directory
Published directory entries matching your search.
ANY.RUN sandbox for interactive malware analysis, behavior monitoring, and file investigation.

Jotti's malware scan is a free service that scans suspicious files with several anti-virus programs. Users can submit up to five files at once, with a 250MB limit per file. Files are shared with anti-virus companies so their products' detection accuracy can be improved.
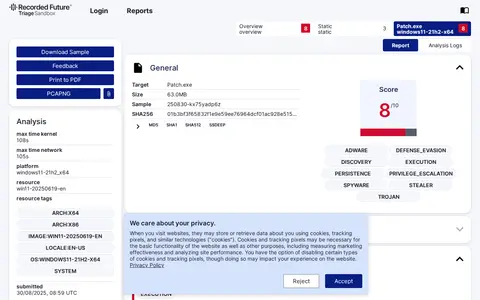
Triage is a malware analysis sandbox for dissecting malware samples, offering a customizable environment with detections and configuration extraction for many malware families. Public reports can be viewed, and a REST-like API is provided for automating sample analysis.
rifteyy is an independent malware analyst from the Czech Republic. The site collects in-depth malware and ransomware analysis reports, reverse engineering breakdowns, and security research. The analyst describes himself as a computer science student, tech support and teacher at a primary school, and a Malware Removal Expert on various forums. Malware removal help is handled through public forums, not through socials or email.
Awesome Malware Analysis is a GitHub repository or organization with source code, releases, documentation, or project resources.
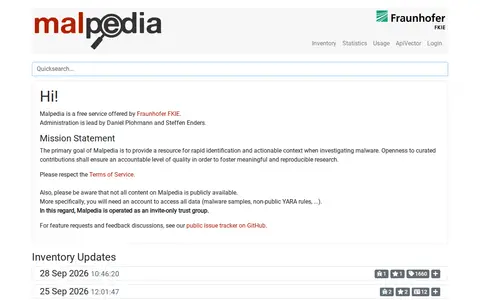
Malpedia is a free service from Fraunhofer FKIE aimed at providing a resource for rapid identification and actionable context when investigating malware. Curated contributions are intended to support accountable quality and reproducible research. Not all content is publicly available; an account is needed to access all data, such as malware samples and non-public YARA rules, and it is operated as an invite-only trust group.

Behavioral1 is a malware sandbox report showing behavior, indicators, and analysis details.
Online service for detailed and free analysis of suspicious files and URLs.
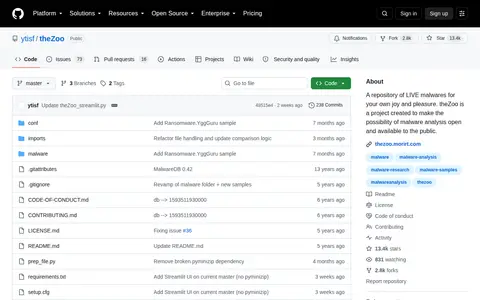
GitHub malware research repository containing live samples for controlled analysis environments.
Community threat intelligence platform for indicators, pulses, malware, and attack research.

Malware research archive with papers, samples, writeups, and historical security material.
Cloud malware scanning page for checking suspicious files against online detection services.
Threat intelligence search platform for malware indicators, IPs, domains, URLs, and hashes.

Historical malware archive mirrored by vx-underground for research and preservation.
A site offering lessons on the fundamentals of reverse engineering, binary analysis and software security. It describes hands-on tutorials, practical examples and real-world scenarios covering binary analysis, malware research, and static and dynamic analysis.
GitHub collection of APT reports, threat actor notes, and security research documents.

Fortinet threat intelligence portal for security updates, IP reputation, malware, and web filtering data.
Bitdefender map showing detected cyber threats, malware activity, and attack trends.
Exploit-DB paper archive with security research, exploitation papers, and technical writeups.
Exploit-DB binary exploit archive for security research and controlled testing.

Fortinet map visualizing cyber attack activity, malware detections, and global threat events.
ImHex supports reverse engineering, malware analysis, file inspection, or security research workflows.
LemmeDebug supports reverse engineering, malware analysis, file inspection, or security research workflows.

REMnux is a Linux toolkit for reverse-engineering and analyzing malicious software. It provides a curated collection of free community-created tools for hands-on malware investigation, distributed as a virtual machine, a from-scratch install on a dedicated host or compatible Ubuntu system, and Docker images of popular analysis tools.