tria.ge
Malware sandbox report documents a safety warning, scam report, malware concern, or risky download example.
Directory
Published directory entries matching your search.
Malware sandbox report documents a safety warning, scam report, malware concern, or risky download example.
Malware sandbox report documents a safety warning, scam report, malware concern, or risky download example.
Malware sandbox report documents a safety warning, scam report, malware concern, or risky download example.
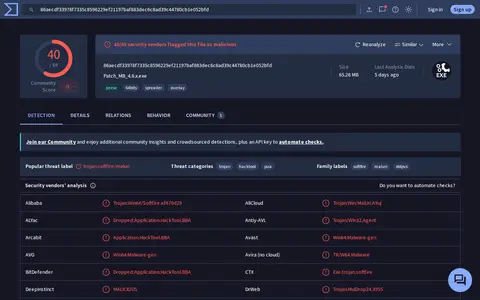
malware documents a safety warning, scam report, malware concern, or risky download example.
Reddit link documents a safety warning, scam report, malware concern, or risky download example.
Reddit link documents a safety warning, scam report, malware concern, or risky download example.

scurvy malware documents a safety warning, scam report, malware concern, or risky download example.
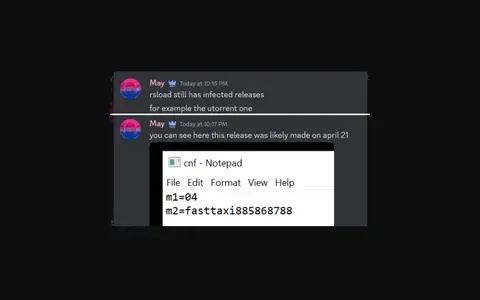
utorrent malware documents a safety warning, scam report, malware concern, or risky download example.
ANY.RUN sandbox for interactive malware analysis, behavior monitoring, and file investigation.

Jotti's malware scan is a free service that scans suspicious files with several anti-virus programs. Users can submit up to five files at once, with a 250MB limit per file. Files are shared with anti-virus companies so their products' detection accuracy can be improved.
rifteyy is an independent malware analyst from the Czech Republic. The site collects in-depth malware and ransomware analysis reports, reverse engineering breakdowns, and security research. The analyst describes himself as a computer science student, tech support and teacher at a primary school, and a Malware Removal Expert on various forums. Malware removal help is handled through public forums, not through socials or email.
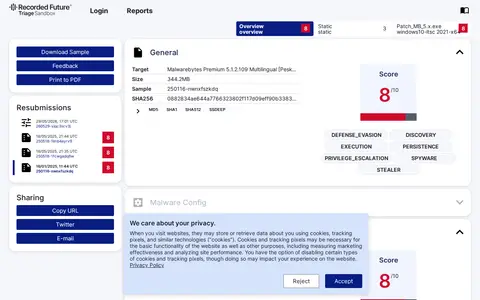
Triage is a malware analysis sandbox for dissecting malware samples, offering a customizable environment with detections and configuration extraction for many malware families. Public reports can be viewed, and a REST-like API is provided for automating sample analysis.
Awesome Malware Analysis is a GitHub repository or organization with source code, releases, documentation, or project resources.

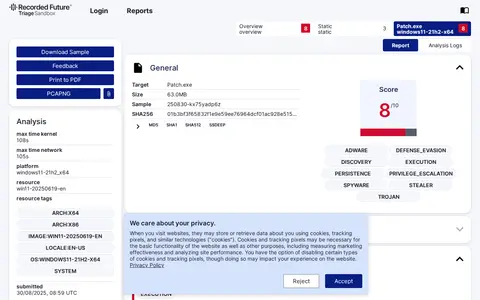
Behavioral1 is a malware sandbox report showing behavior, indicators, and analysis details.
caught with malware is a text reference page with notes, links, warnings, or organized update details.
Malpedia is a free service from Fraunhofer FKIE aimed at providing a resource for rapid identification and actionable context when investigating malware. Curated contributions are intended to support accountable quality and reproducible research. Not all content is publicly available; an account is needed to access all data, such as malware samples and non-public YARA rules, and it is operated as an invite-only trust group.

Malwarebytes is a Linux, macOS, BSD, or Unix resource for tools, documentation, communities, or system workflows.
Malwarebytes is a privacy tool for blocking ads, trackers, popups, proxies, or unwanted web behavior.
Malwarebytes Forums is a privacy tool for blocking ads, trackers, popups, proxies, or unwanted web behavior.

Security Arena is a forum section on Sysnative Forums for help removing viruses, trojans and other malware. It contains new threads and locked or solved threads, and a sticky post gives malware removal posting instructions. Threads on the page cover topics such as virus infections, possible RAT or malware concerns, and slow machines.
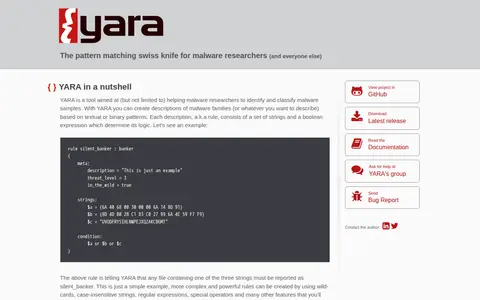
YARA is a tool aimed at helping malware researchers identify and classify malware samples. It creates descriptions of malware families, called rules, based on textual or binary patterns; each rule consists of strings and a boolean expression. YARA is multi-platform, running on Windows, Linux and Mac OS X, and can be used via its command-line interface or from Python scripts with the yara-python extension.
Community threat intelligence platform for indicators, pulses, malware, and attack research.
constant popups documents a safety warning, scam report, malware concern, or risky download example.
Microsoft Safety Scanner is a scan tool designed to find and remove malware from Windows computers. It only scans when manually triggered, is a portable executable, and expires 10 days after being downloaded. It supports Windows client and server versions and does not replace an anti-malware product.