Directory

Search results

Published directory entries matching your search.

Search results

37 listings
Preview unavailable
javadecompilers.com

JavaDecompiler provides an online interface for extracting source code from .class and .jar binary files. It presents several Java decompilers, including CFR, JD, Procyon, Fernflower and JAD, with notes on each. The site also links to an APK decompiler and a knowledge base. JAD is listed for historical reasons only.
Programming Languages 0
github.com

jd-gui is a GitHub repository or organization with source code, releases, documentation, or project resources.

Programming Languages 0
guyinatuxedo.github.io

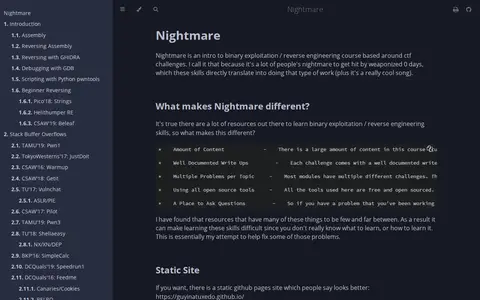
Nightmare is an introductory course on binary exploitation and reverse engineering built around CTF challenges. Its materials are structured linearly and include documented write-ups for each challenge, with most modules offering multiple problems per topic so learners can apply an attack technique to different iterations. The course uses only free and open source tools, and its static site is built with mdbook.

Programming & Technology Learning 0
onlinedisassembler.com

Online disassembler for inspecting executable files and assembly output during reverse engineering.

Security Tools & Toolkits 0
overthewire.org

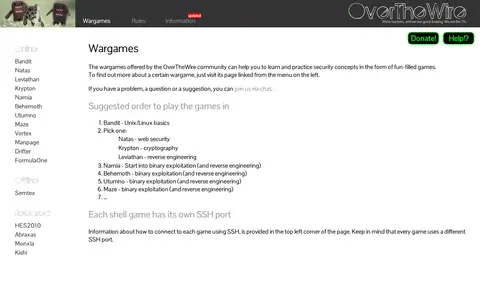
OverTheWire is a community offering wargames intended to help people learn and practice security concepts through games. Its suggested order begins with Bandit for Unix/Linux basics, followed by a choice among Natas for web security, Krypton for cryptography or Leviathan for reverse engineering, then binary exploitation games. Each shell game uses its own SSH port.

Programming & Technology Learning 0
Preview unavailable
pretendo.network

Pretendo Network is a free and open source replacement for Nintendo's servers for the 3DS and Wii U, built through clean-room reverse engineering. It aims to preserve online functionality for those consoles, and Cemu 2.1 officially supports it under network account options. Connecting on consoles requires hacks such as Aroma for Wii U and Luma3DS for 3DS, though Wii U also has a limited hackless SSSL method.

Game Tools & Utilities 0
remnux.org

REMnux is a Linux toolkit for reverse-engineering and analyzing malicious software. It provides a curated collection of free community-created tools for hands-on malware investigation, distributed as a virtual machine, a from-scratch install on a dedicated host or compatible Ubuntu system, and Docker images of popular analysis tools.

Security Tools & Toolkits 0
rifteyy.org

rifteyy is an independent malware analyst from the Czech Republic. The site collects in-depth malware and ransomware analysis reports, reverse engineering breakdowns, and security research. The analyst describes himself as a computer science student, tech support and teacher at a primary school, and a Malware Removal Expert on various forums. Malware removal help is handled through public forums, not through socials or email.

Malware Protection 0
rizin.re

Rizin is a free and Open Source Reverse Engineering Framework. It uses a shell-like command-line environment for analyzing binaries, with automatic signature detection to match unnamed functions against FLIRT signatures. Projects for saving and loading Rizin sessions are in beta, and Cutter is Rizin's official graphical user interface. A package manager for downloading, compiling and installing plugins is still in early development.

Security Tools & Toolkits 0
github.com

Snapchat gRPC protobuf reverse engineering tool ( Login 2026 )

Snapchat 0
github.com

TikTok Reverse Engineering Documentation.

TikTok 0
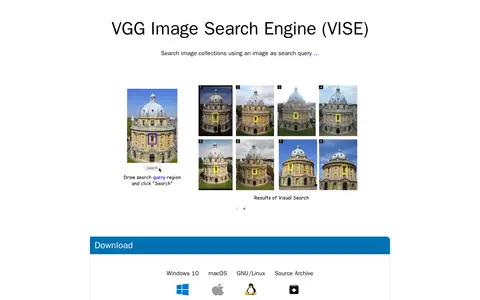
robots.ox.ac.uk

VISE is a standalone open-source visual search application developed by the Visual Geometry Group in Oxford University's Department of Engineering Science. It enables visual search of large image collections using an image as a query. Installers are available for Windows 10, macOS, and Linux, with source code provided for compilation.

Image & Media Search 0
x86re.com

x86re hosts a series of reverse engineering articles. Part 1 gives a brief introduction to RE, executables, compiling, 32-bit x86 syntax, and stack frames. Part 2 covers Portable Executable image file headers and sections.

Programming & Technology Learning 0