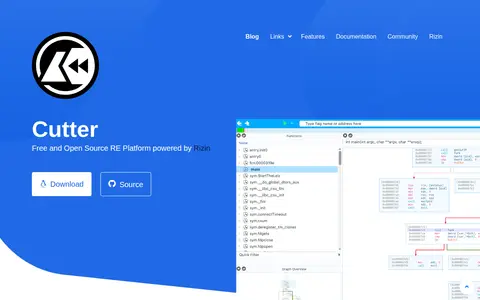
Cutter is a free and open-source reverse-engineering platform powered by Rizin, using Rizin as its core engine. It is built with Qt and C++ and provides access to Rizin features through a GUI or an integrated terminal. Its releases integrate the native Ghidra decompiler, and it includes a graph view, debugger (beta), hex editor, Python scripting engine and plugins.
Directory
Search results
Published directory entries matching your search.
Frida is a dynamic instrumentation toolkit for developers, reverse-engineers and security researchers. It lets users inject their own scripts into black box processes to hook functions and trace application code, and it runs on Windows, macOS, GNU/Linux, iOS, watchOS, tvOS, Android, FreeBSD and QNX.
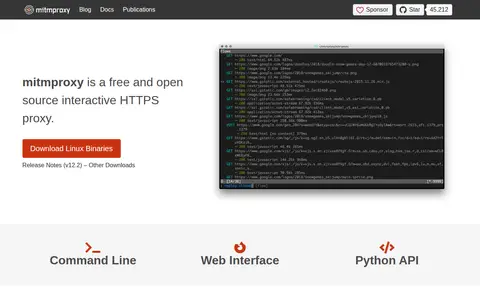
mitmproxy is a free and open source interactive HTTPS proxy. It can be used to intercept, inspect, modify and replay web traffic, including HTTP/1, HTTP/2, HTTP/3, WebSockets and other SSL/TLS-protected protocols. It offers a command line interface, a graphical web interface, and a Python API for writing addons and scripts. Downloads are available for Windows, Linux, macOS and Docker.
A project providing Markdown templates for Offensive Security exam reports, covering exams including OSCP, OSWE, OSCE, OSEE and OSWP. It aims to replace LaTeX, Microsoft Office Word and LibreOffice Writer for report writing. Report generation uses a script and requires Pandoc, LaTeX and p7zip. Optional Pandoc Lua filters can be passed.
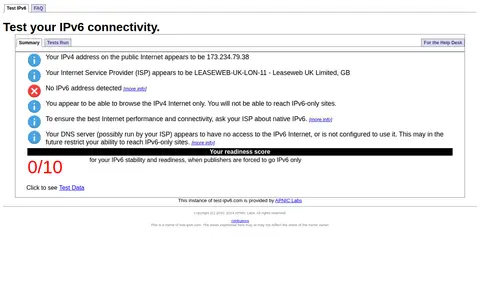
Test IPv6 tests a browser and connection for IPv6 readiness and shows the current IPv4 and IPv6 address. The site requires JavaScript and the ability to pull in cross-site scripts to perform the testing. A simple test offers a quick pass/fail for IPv4, IPv4+IPv6, and IPv6, but provides little diagnostic information.
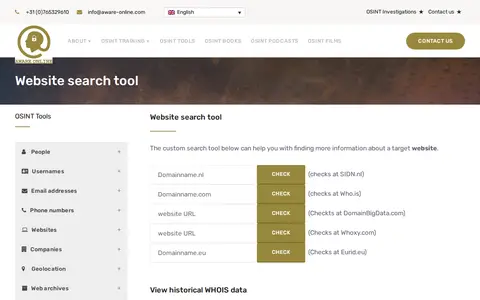
A custom OSINT tool from Aware Online Academy for investigating a target website. It provides scripts to view historical WHOIS data, check website text and source code on third-party sites, visualise links, map web pages, check Reddit presence, find open FTP ports and find other top level domains.
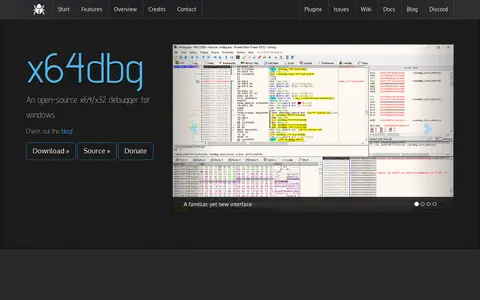
x64dbg is an open-source debugger for Windows that supports both x64 and x32 applications through a single interface. It offers full-featured debugging of DLL and EXE files, a plugin API, an integrated scripting language and customizable themes.
YARA is a tool aimed at helping malware researchers identify and classify malware samples. It creates descriptions of malware families, called rules, based on textual or binary patterns; each rule consists of strings and a boolean expression. YARA is multi-platform, running on Windows, Linux and Mac OS X, and can be used via its command-line interface or from Python scripts with the yara-python extension.