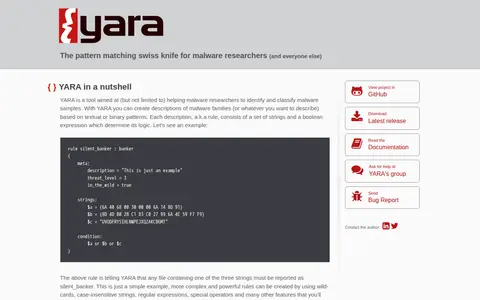
YARA is a tool aimed at helping malware researchers identify and classify malware samples. It creates descriptions of malware families, called rules, based on textual or binary patterns; each rule consists of strings and a boolean expression. YARA is multi-platform, running on Windows, Linux and Mac OS X, and can be used via its command-line interface or from Python scripts with the yara-python extension.
Directory
Search results
Published directory entries matching your search.
Python package template for building command-line OSINT tools with a reusable project structure.
Google notebook environment for running Python code, experiments, data analysis, and research workflows.
Python OSINT crawler for extracting URLs, files, endpoints, and related website data.
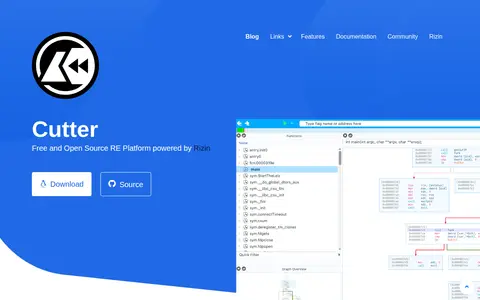
Cutter is a free and open-source reverse-engineering platform powered by Rizin, using Rizin as its core engine. It is built with Qt and C++ and provides access to Rizin features through a GUI or an integrated terminal. Its releases integrate the native Ghidra decompiler, and it includes a graph view, debugger (beta), hex editor, Python scripting engine and plugins.
mitmproxy is a free and open source interactive HTTPS proxy. It can be used to intercept, inspect, modify and replay web traffic, including HTTP/1, HTTP/2, HTTP/3, WebSockets and other SSL/TLS-protected protocols. It offers a command line interface, a graphical web interface, and a Python API for writing addons and scripts. Downloads are available for Windows, Linux, macOS and Docker.
Python tool that identifies hashes, emails, IPs, URLs, and other strings found in text or files.
unblob is an extraction suite that parses unknown binary blobs for more than 30 archive, compression and file-system formats. It extracts content recursively and carves out unrecognized chunks. It is free under the MIT license, offers a command line interface and can be used as a Python library. It was developed and is maintained by ONEKEY.