MalwareBazaar is a platform from abuse.ch and Spamhaus for sharing malware samples with the infosec community, antivirus vendors, and threat intelligence providers. Users can upload samples, browse the database, set alerts for newly observed malware, and use APIs to push or pull signals and automate bulk queries. Spamhaus datasets enhanced with MalwareBazaar samples are also available.
Directory
Search results
Published directory entries matching your search.
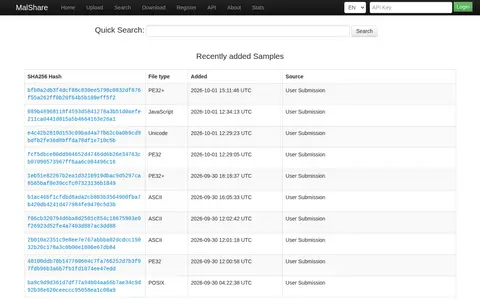
MalShare is a community-driven public malware repository that provides free access to malware samples and tooling for the information security community. The site lists recently added samples with SHA256 hashes, file types and submission sources, and offers upload, search, download and API sections along with registration.
Malware research archive with papers, samples, writeups, and historical security material.
Malpedia is a free service from Fraunhofer FKIE aimed at providing a resource for rapid identification and actionable context when investigating malware. Curated contributions are intended to support accountable quality and reproducible research. Not all content is publicly available; an account is needed to access all data, such as malware samples and non-public YARA rules, and it is operated as an invite-only trust group.
GitHub malware research repository containing live samples for controlled analysis environments.
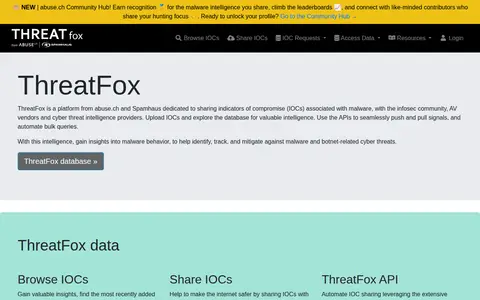
ThreatFox is a project from abuse.ch and Spamhaus for sharing indicators of compromise associated with malware with the infosec community, AV vendors and cyber threat intelligence providers. Users can upload IOCs, browse the database, and use APIs to push and pull signals and automate bulk queries. Spamhaus datasets are enhanced with malware samples from ThreatFox.
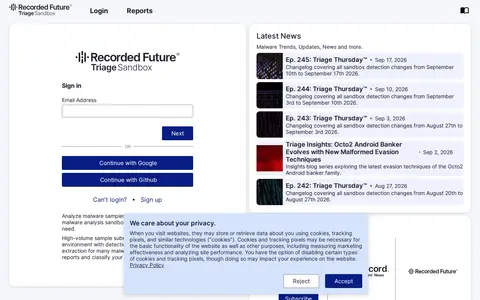
Triage is a malware analysis sandbox for dissecting malware samples, offering a customizable environment with detections and configuration extraction for many malware families. Public reports can be viewed, and a REST-like API is provided for automating sample analysis.
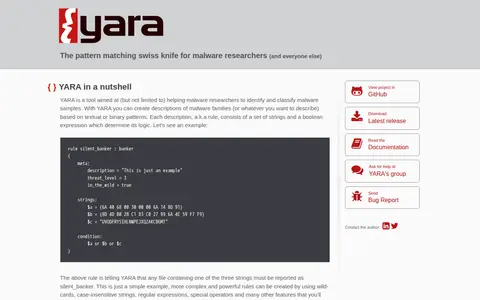
YARA is a tool aimed at helping malware researchers identify and classify malware samples. It creates descriptions of malware families, called rules, based on textual or binary patterns; each rule consists of strings and a boolean expression. YARA is multi-platform, running on Windows, Linux and Mac OS X, and can be used via its command-line interface or from Python scripts with the yara-python extension.