Sandboxie-Plus is open source sandbox-based isolation software for 32-bit and 64-bit Windows NT-based operating systems. It creates an isolated operating environment in which applications can be run or installed without permanently modifying the local or mapped drive, allowing controlled testing of untrusted programs and web surfing. Development has continued under David Xanatos since the project became open source. Two builds exist: Classic with an MFC-based UI and Plus with a Qt-based UI.
Directory
Search results
Published directory entries matching your search.
Security / Antivirus Multireddit is a Reddit community or thread with discussion, guides, updates, or shared resources.
Security Arena is a forum section on Sysnative Forums for help removing viruses, trojans and other malware. It contains new threads and locked or solved threads, and a sticky post gives malware removal posting instructions. Threads on the page cover topics such as virus infections, possible RAT or malware concerns, and slow machines.
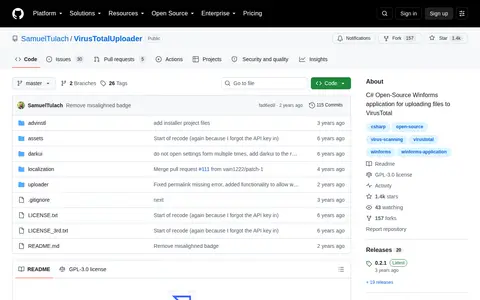
Uploader is a code project with source, releases, documentation, or setup notes.
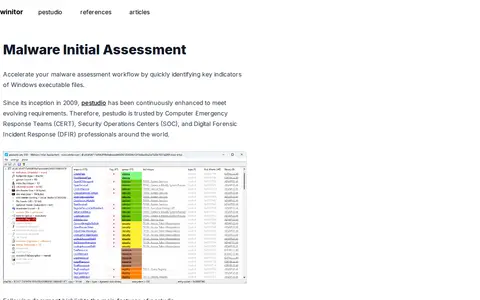
Winitor's pestudio is a malware initial assessment tool. It helps identify key indicators of Windows executable files to speed up malware assessment workflows. The page states it has been enhanced since 2009.
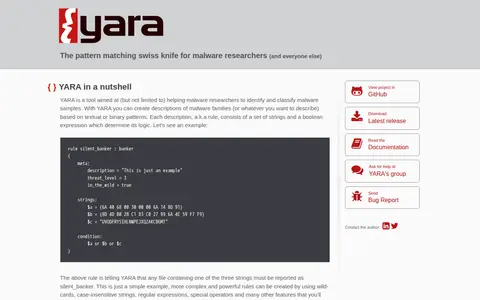
YARA is a tool aimed at helping malware researchers identify and classify malware samples. It creates descriptions of malware families, called rules, based on textual or binary patterns; each rule consists of strings and a boolean expression. YARA is multi-platform, running on Windows, Linux and Mac OS X, and can be used via its command-line interface or from Python scripts with the yara-python extension.
Zulu is a dynamic risk scoring engine for web-based content, presented on Zscaler's site. The page asks how safe a web destination is and links to Zscaler security solutions and products.