A guide to running Lyncis, a webkit-based jailbreak for 32-bit iOS devices on firmware versions 7.1 to 7.1.2. It describes opening Safari, visiting the Lyncis website and tapping "Jailbreak", and notes that users can retry if the exploit fails.
Installing Palera1n
A guide on installing palera1n, a jailbreak compatible with A11 and earlier devices on iOS 15.0 and later. It covers installation on macOS and Linux, including running commands and entering DFU mode, with warnings about passcode and SEP functionality on A11 devices.
Features
- compatible with A11 (iPhone X) and earlier devices on iOS 15.0 and later Source: ios.cfw.guide
Links
Tags
-
0
A guide to running Lyncis, a webkit-based jailbreak for 32-bit iOS devices on firmware versions 7.1 to 7.1.2. It describes opening Safari, visiting the Lyncis website and tapping "Jailbreak", and notes that users can retry if the exploit fails.
-
0
A guide to installing greenpois0n, an untethered jailbreak that survives a reboot and can cause a permanent bootloop if something goes wrong. It covers every iOS device except the iPhone 3G on firmware versions 4.1, 4.2.1, and 4.2.6, plus the iPad 1st Generation on version 3.2.2, and requires a computer running macOS 10.11 or older or Windows XP through 8.1.
-
0
A guide to installing TrollStore, a utility that permanently signs and installs applications with almost any entitlement using a CoreTrust bug. Installation varies by device and iOS version, and some firmware versions are never supported. TrollStore is not a jailbreak.
-
0
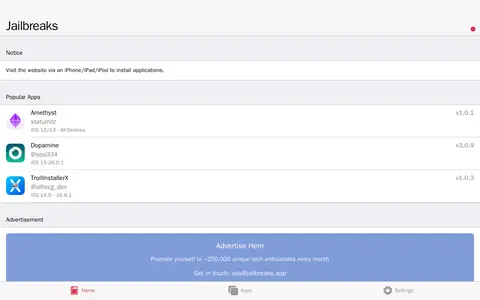
Jailbreaks.app is a website that offers jailbreaks to download for free without a computer. It states that installation requires visiting the site on an iPhone, iPad or iPod. As of the page, the site is revoked: apps downloaded from it will not open unless the device is jailbroken and using AppSync, though users can obtain their own certificate from partner FlareStore to sign apps.
-
0
Pangu933 is a jailbreak tool for every 64-bit iOS device on firmware 9.2 through 9.3.3. It is not persistent, so the exploit must be re-run after each reboot; the guide describes rejailbreaking through a website. The application is installed with PlumeImpactor, and the guide also covers certificate updates and crash retries.
-
0
A guide to installing the Socket jailbreak application on 32-bit iOS devices running firmware 10.0.1 through 10.3.4. Socket is generally untethered, requiring the exploit to be run once, though on the iPad 4th Generation with firmware 10.3.2 to 10.3.4 the untether must be enabled in the app and carries a boot issue risk. Installation uses PlumeImpactor or jailbreaks.app.
Community notes
Reviews and discussion
No reviews yet
Be the first to share how this project worked for you.
Join the discussion
Sign in with a verified account to leave a review or join the discussion.
Sign in to review